
White-box: Sees your code and app at once
Topscan reads your code and attacks your live app at once. It knows where to look and finds what outside-only tests miss
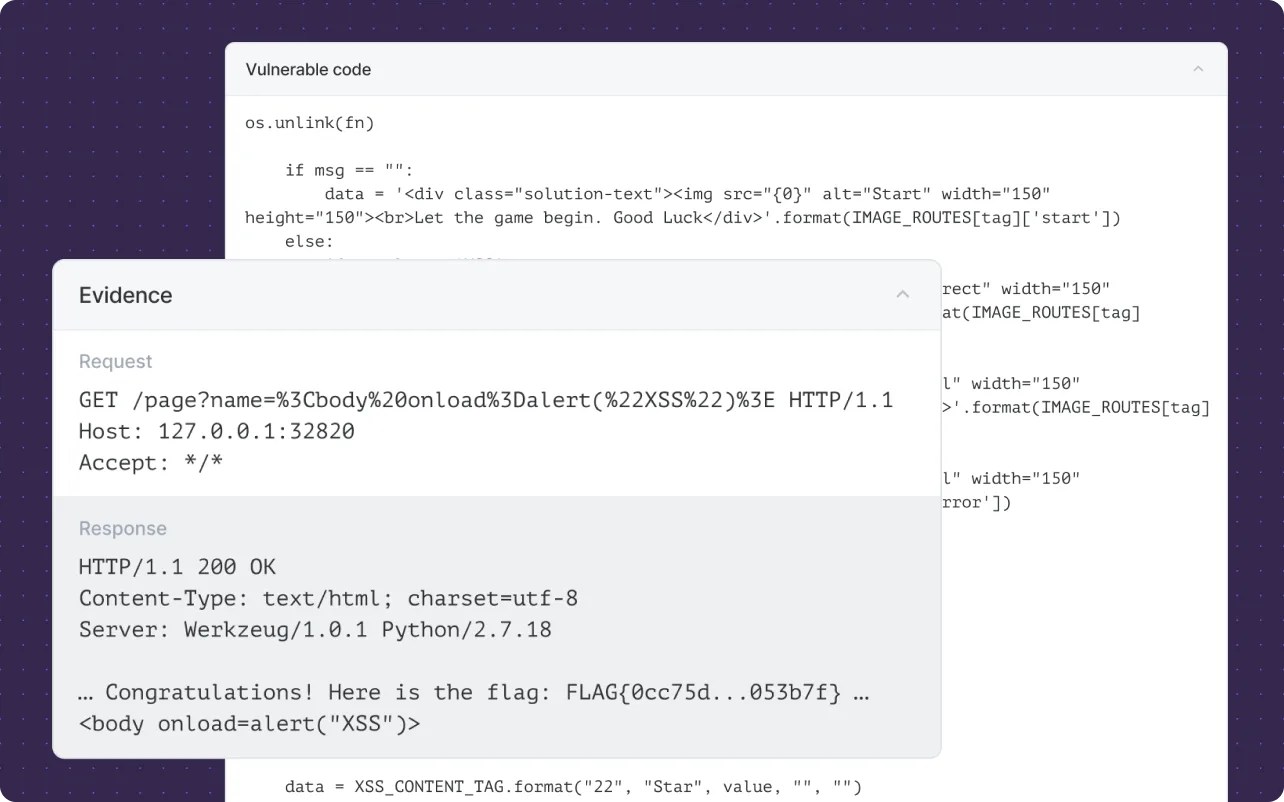
Scanners guess. AI Pentest checks for real: it reads your code, attacks your live app, and shows the exact request and response behind every finding
From $200 · Results in hours · Your code stays private
"Can we actually be broken into?" Between the annual audit and daily deploys, most teams have no answer.
Hundreds of unverified alerts
$1000+ per manual pentest
Weeks of scoping calls
Tested only once a year
Tools that never see your code
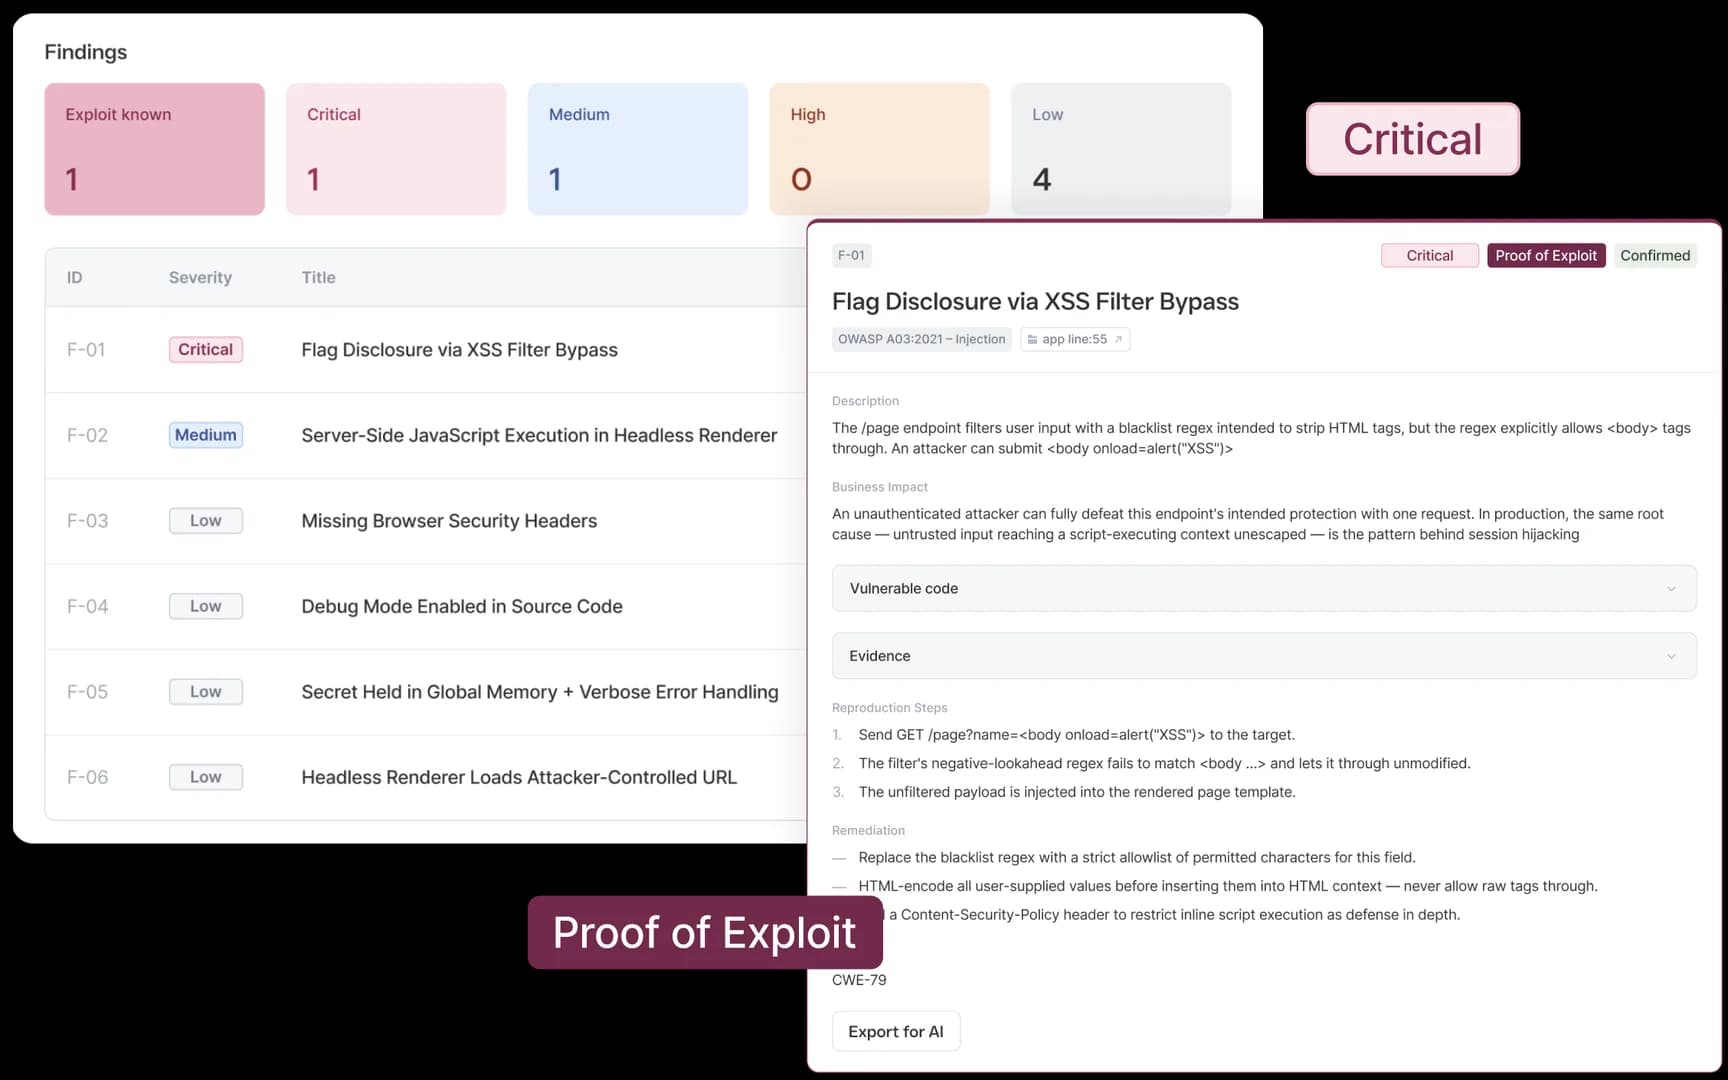
Only proven findingsEach one comes with a working exploit
From $200, fixed priceYou see the price before you start
Report in about 2 hoursLaunch from the dashboard in minutes
Run it before every releaseFast and affordable enough for every update
Code + live appTests like a real pentester with full access
Cobalt Autonomous Pentest
$3,500
per test — findings in 24 hours
cobalt.io/platform/pricing checked 02.10.2026
Ethiack On-Demand
€3,000
per test — report within 5 days
ethiack.com/pricing, checked 02.10.2026
Topscan AI Pentest
from $200
per test — report in about two hours
Four tiers by codebase size. Duration: a typical test
A short setup wizard. No scoping calls, no vendor, no waiting for a slot
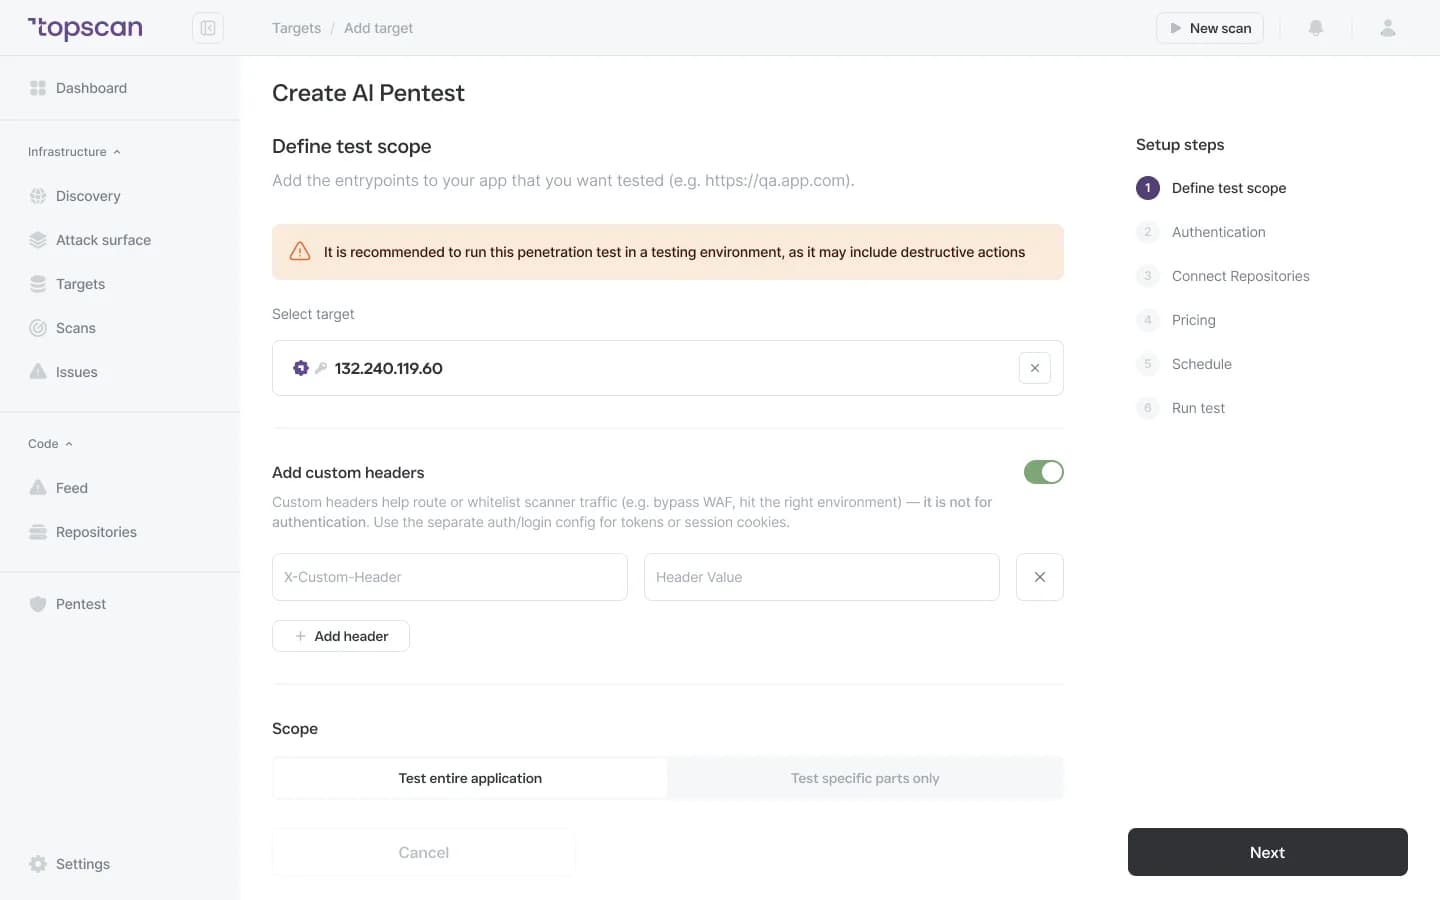
Step 1 · Target
Choose from the domains you've already added and verified in Topscan — you can only test what you own. We recommend pointing it at a staging or test environment rather than production.
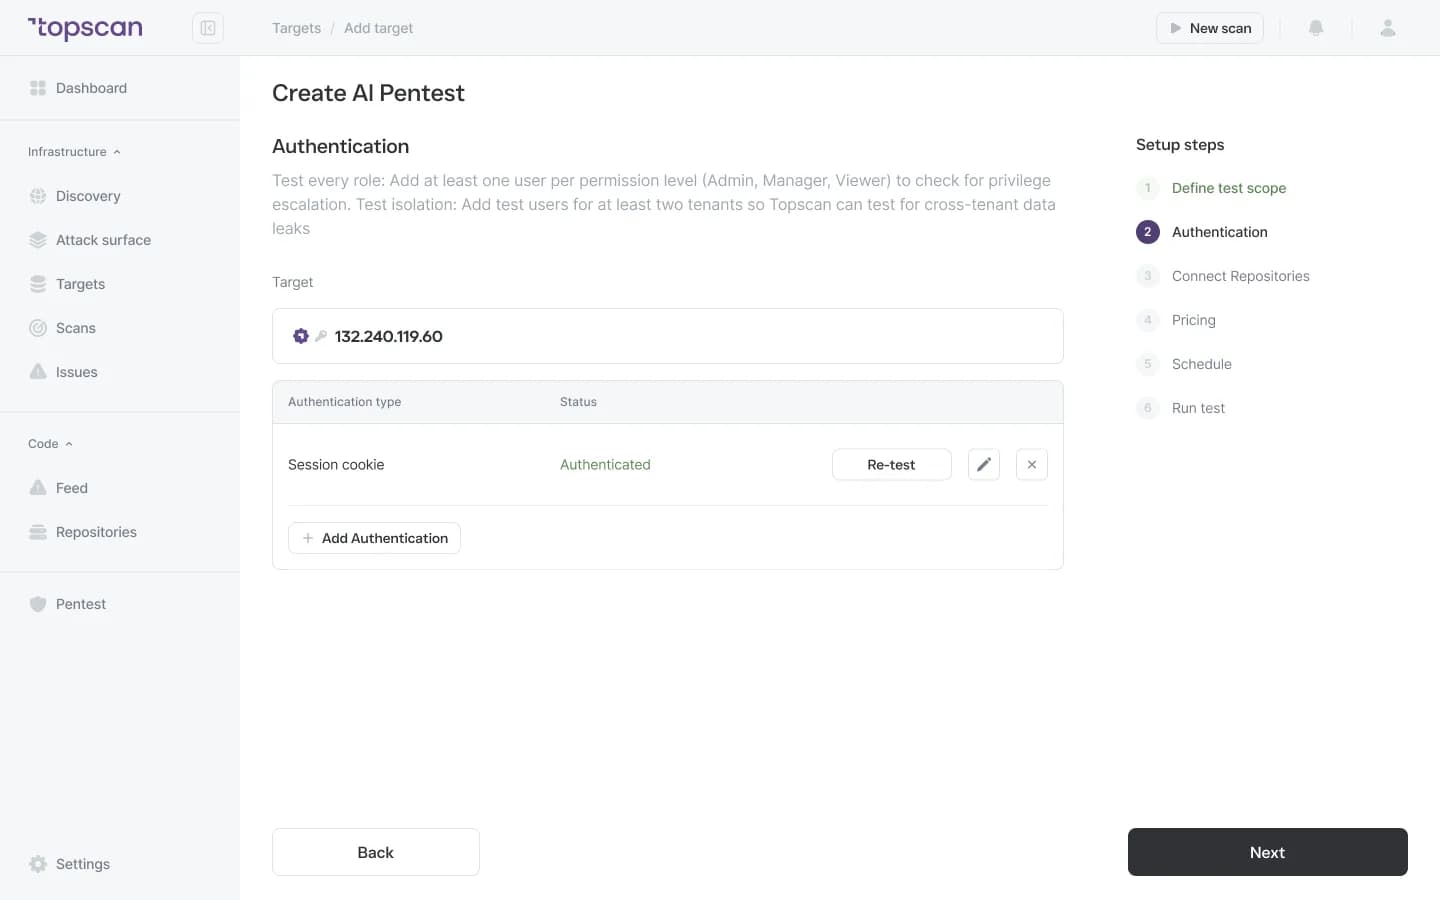
Step 2 · Authorization
Give the agent accounts for an admin, a regular user, and users from different customers. It will test the mistakes that cost SaaS companies the most: privilege escalation and one tenant seeing another tenant's data
Step 3 · Code
AI Pentest is a white-box test: the agent studies your source code to understand how the application works from the inside, then verifies its hypotheses against the live app. It also uses the results of your existing Topscan code and application scans as a starting map — you don't describe your application to anyone.
Full code analysis runs on Topscan's own GPU servers.
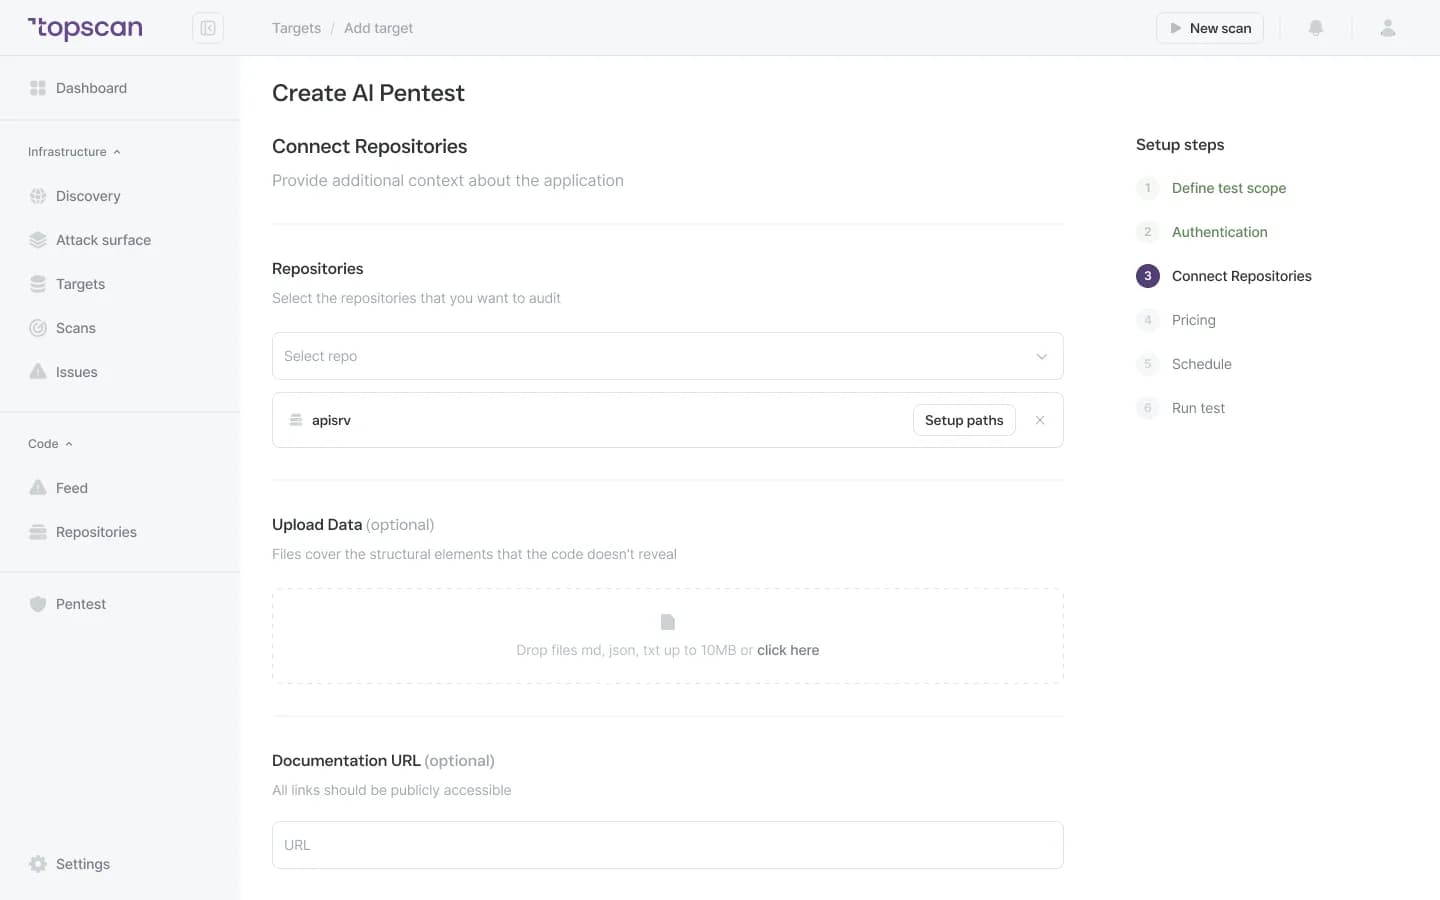
Step 4 · Price & run
The price is calculated from the size of your codebase and shown before launch. It doesn't depend on the size of your website and doesn't change mid-test. Run now or schedule a window — working hours, overnight or the weekend — and follow the progress in real time.
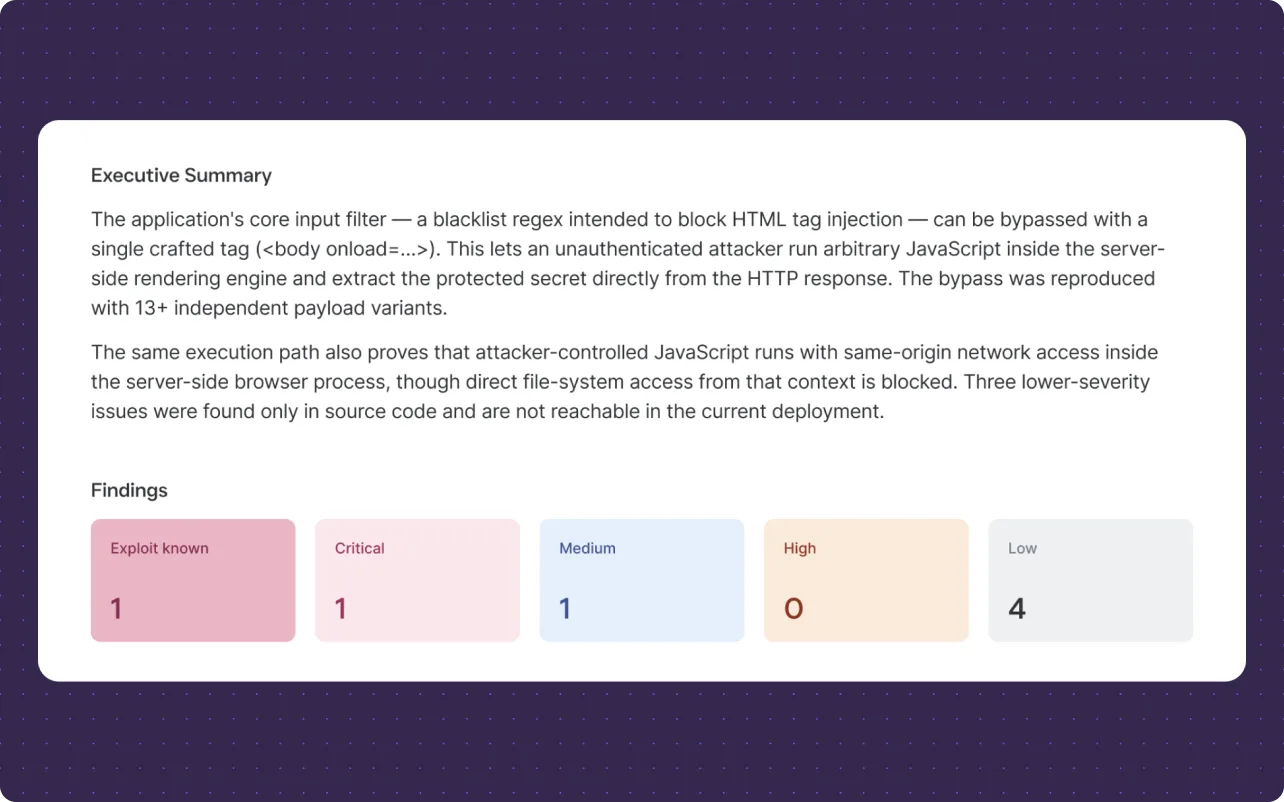
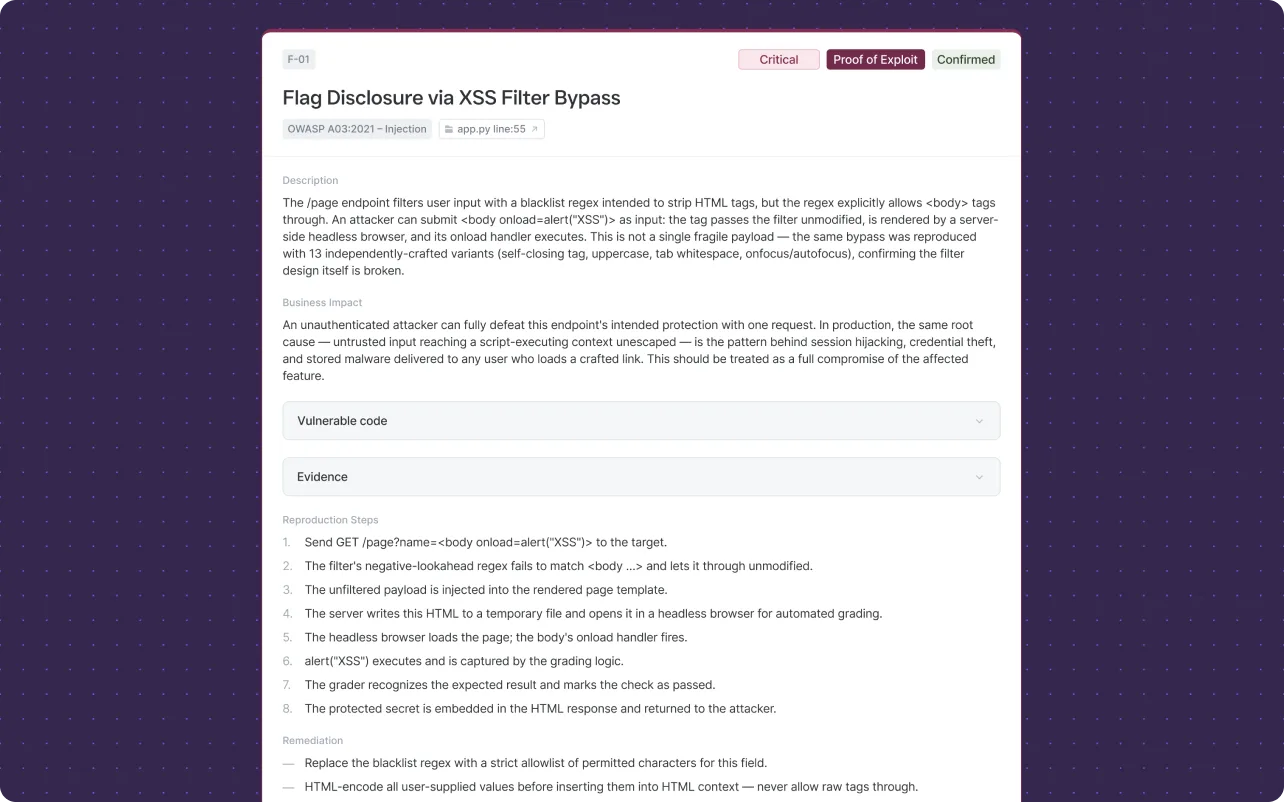
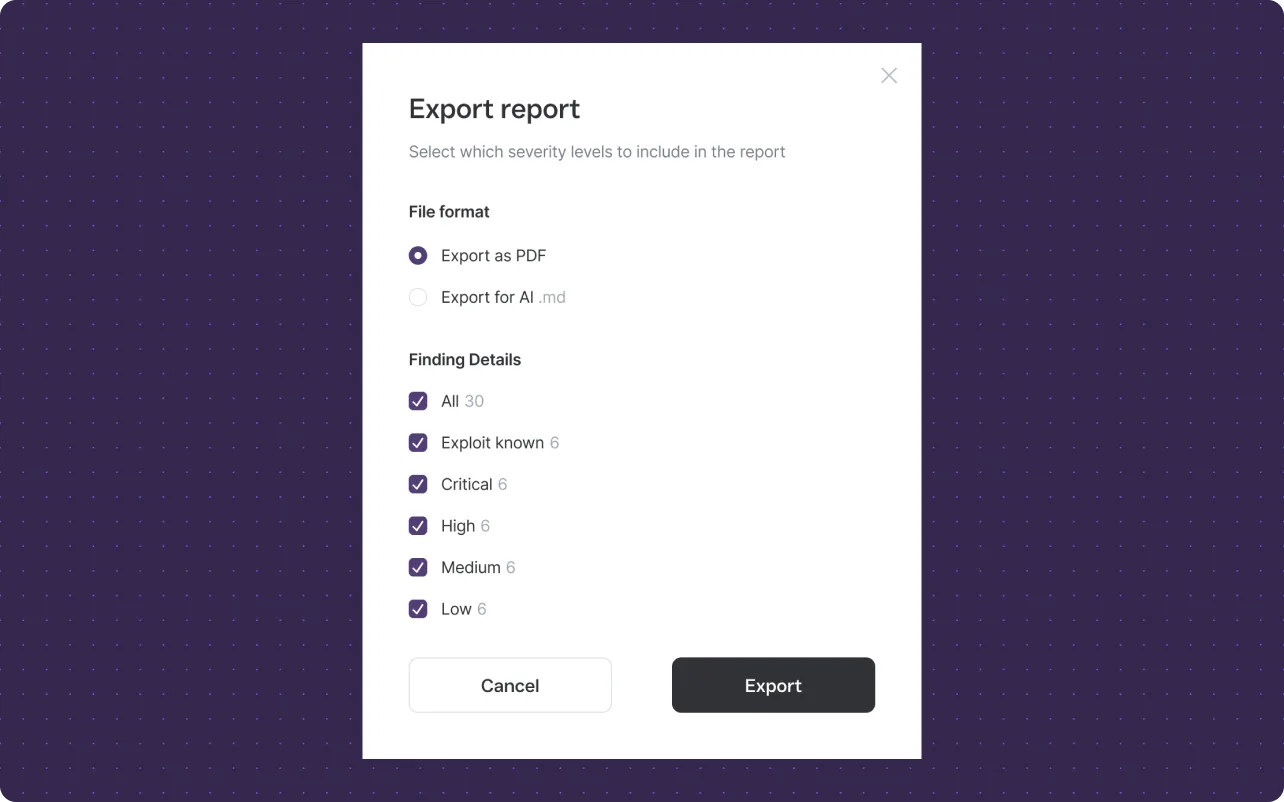
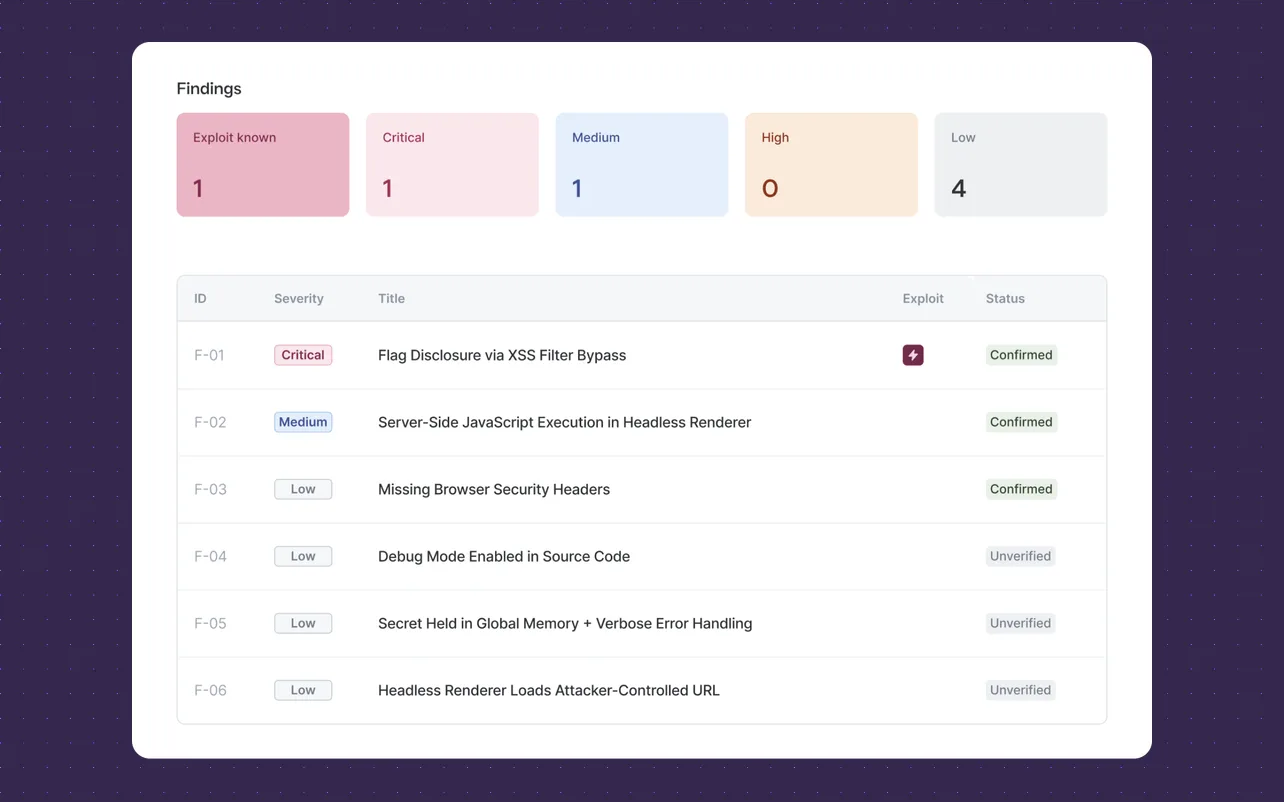
Your team sees what to fix first, your auditor gets the proof, and your AI coding tool gets everything it needs to fix it
Every finding sorted from Critical to Low, so you fix the worst first. Issues found only in code are marked Unverified
1of5
Without dedicated security resources, teams struggle to maintain visibility into their attack surface and respond to vulnerabilities before they're exploited.
Topscan reads your code and attacks your live app at once. It knows where to look and finds what outside-only tests miss
Each one is proven with a real request and response and double-checked outside the AI. Code-only issues are marked Unverified
The pentest builds on the code and app scans you already run in Topscan. No briefing a vendor, no explaining your setup. It's all there.
We analyze it on our own GPU servers. Nothing goes to outside AI providers or contractors
Our agent captured the flag in 98 of the 104 web challenges of XBEN — the open benchmark XBOW released in 2024.
Here's what that number does and doesn't tell you.
98/104 challenges solved
Internal run, July 2026
xbow-engineering/validation-benchmarks
What it shows
The agent doesn't stop at flagging a weakness — it exploits it end to end across common web vulnerability classes: injection, XSS, SSRF, access control and more.
What it doesn't
The set is public, and its author notes that leading tools now score close to 100% on it. It's a baseline, not a ranking — and a pass-or-fail benchmark says nothing about false positives.
Why your report doesn't rely on it
A score is about someone else's app. In your report, every confirmed finding carries its own proof — the request and the response from your application.
Clients ask for a pentest, and agencies quote thousands. Get proven results from $200
Check every big release, not just once a year. Launch in minutes, get results in hours.
Can a user act as admin? Can one customer see another's data? We test both in one run.
Pick the size that matches your app and pay once per test. Your Topscan plan already covers code, infrastructure and web app scanning
Small
$200
Small application, single repository
Medium
$400
Typical product, a few repositories
Large
$800
Large codebase across many repositories
XL
$1,500
The biggest codebases, many repositories
Paid in tokens. 1 token = $1. Purchased tokens never expire
Tokens pay for pentests and for SAST AI features: Autofix and PR Review. Basic includes 100 tokens a month. Pro includes 300, which covers a Small pentest. Tokens you buy never expire. Cancel a test before it starts, and all its tokens come back